

PHP2Shell: why European governments took sites offline
Two PHP flaws rated 9.2 out of 10 pushed governments from the Netherlands to Finland to pull websites offline. Here is what happened and what to check if you run a site.
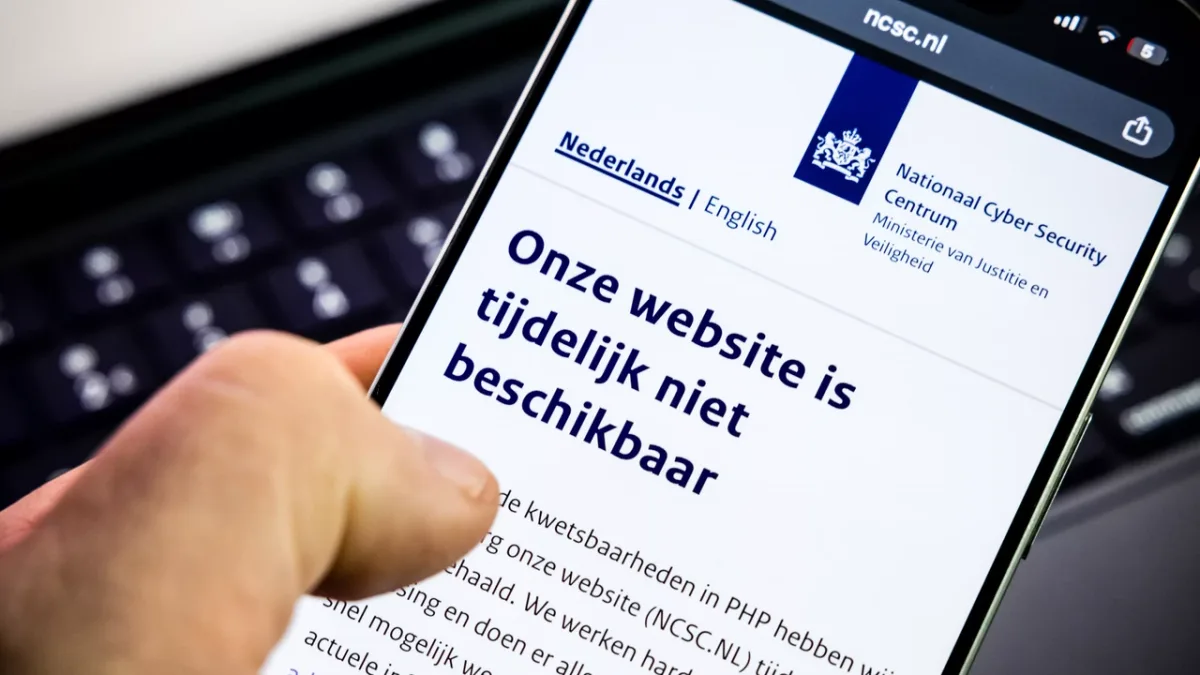
Why did the Netherlands shut down the website of its own National Cyber Security Centre? Because two bugs in PHP let someone on the internet take over the commands on your server, with no password and no account. Patches came out on Wednesday, October 21, 2026, and many governments did not wait to install them.
What is PHP2Shell and how serious is it?
The two vulnerabilities carry the identifiers CVE-2026-109618 and CVE-2026-109619, and together they are called PHP2Shell. Each is rated 9.2 out of 10 on the CVSS v4.0 scale. According to the European cybersecurity team CERT-EU, a rating like that means remote code execution without logging in: an attacker can plant a malicious program, read files on the server and get into the database.
Every PHP installation that serves web requests is affected: PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. The patched versions are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
According to the web survey service W3Techs, PHP runs almost 70 percent of the sites whose language can be determined, including WordPress. The organization Censys counted about 2.6 million servers, and about 1.5 million of them run a PHP version for which no patch exists.
Tiffany Faris, interim executive director of the Drupal Association, said: “Every server using any version of PHP released in the last 20 years will be vulnerable.” She added: “This problem affects most of the internet.”
Who took their sites offline?
The list is long, and each country handled it in its own way:
- The Netherlands: the National Cyber Security Centre preventively shut down its own website. The Port of Rotterdam, the government portal Overheid.nl, the football association KNVB, the sites of the five biggest parties and several hospitals followed. Prime Minister Rob Jetten said he was closely following the situation.
- Denmark: the municipal IT company Kombit switched off several services, including the national platform for communication with schools.
- Finland: the state IT supplier Valtori switched off the public internet services of government institutions.
- France: the Interior Ministry put its sites into preventive maintenance, according to Reuters, and the sites of prefectures were taken down as well.
- Germany: the federal IT service ITZBund took down several sites as a precaution.
- Belgium: the Foreign Ministry pulled its sites.
- Czech Republic: the government went offline at 7 p.m. local time, on the advice of its cyber watchdog.
Parts of Wikipedia, the Internet Archive, the website of the Dutch parliament and the city administration of Edinburgh were also taken down temporarily, and some BBC pages went dark. No government has reported a breach or given a date for full restoration of services.
CERT-EU, the British NCSC, Sweden’s CERT-SE and the American National Security Agency (NSA) advised that sites that cannot be patched right away should be disconnected from the network. In its statement the NSA said: “If an urgent update is not feasible, organizations are recommended to take the system offline.”
How did the timeline unfold?
The bugs sat in the code for more than ten years. They were found by the firms Calif and Wiz, as part of the OpenAI project “Patch the Planet”, which hunts for bugs with artificial intelligence tools.
- August 1: Calif found a flaw with the help of a large language model.
- August 11: Calif, working with OpenAI and using the GPT-5.6 Sol model, reported the first flaw to PHP.
- August 24: Wiz, a company owned by Google, independently found flaws and reported the second one, also with AI help. It worked with the Wiz Atlas tool and the Gemini 4 Argon and GPT-5.6 Sol models.
- October 17: Amazon’s security team recorded the first attack attempt against a decoy system, four days before public disclosure.
- October 20, around 3 p.m. UTC: the vulnerability identifiers began circulating publicly, and no patch existed yet.
- October 21, 2 p.m. UTC: coordinated release of the patches, moved back from the previous day because distributors had not managed to package the fix.
That leaves roughly 23 hours in which a public warning existed without a patch anyone could install. Details leaked on social media before the agreed release, so the PHP Foundation issued its statement and patch earlier. The White House says it was notified of the flaw on Friday.
Wiz described its findings as being “among the most severe vulnerabilities discovered in PHP, and probably in the history of software”. The administration of Donald Trump said it “is monitoring and coordinating work with federal agencies and leading AI labs to speed up the release of a fix”, in a statement reported by Reuters.
Is the flaw already being exploited?
Amazon says yes. Several actors attempted attacks on Wednesday as well, before the embargo expired, and Amazon describes the vulnerabilities as “now being widely exploited in the wild”. The company did not know, though, whether those attempts would have worked on real sites.
Matthew Prince, chief executive of Cloudflare, says that more than a million exploitation attempts have been recorded worldwide since the bug surfaced. Cloudflare saw attack traffic aimed at its customers even before the fix was published.
Costin Raiu of TLP:Black judged that artificial intelligence is setting off an “exploitation race”, and that the next step could be “mass compromise of every vulnerable web server on the internet”. Lukas Olejnik, a visiting senior research fellow at King’s College London, said: “The scale is enormous and, with AI, exploitation could happen instantly.”
Japanese Prime Minister Sanae Takaichi urged site owners on X to check whether they use PHP and to get ready for a new patch.
What should you check if you run a site?
Small sites are the most exposed, the ones run by individuals without a security team, often on shared hosting where they do not manage the server. Automattic says users of WordPress.com and Tumblr are protected.
If your site runs on its own WordPress, keep in mind the warning from Wordfence: the usual automatic updates will not apply this fix. Check which PHP version your hosting uses and compare it with the patched numbers in this article. If you cannot update right away, the agencies recommend taking the site offline for the time being.


